Protect Data
DSAR Automation
Subject access requests answered inside your own environment: collection, de-duplication, and redaction automated, every legal judgement left to your people, and every decision logged.
- The requester’s data protected
- Redaction you can defend
- Photographs, video, and audio
- A record the ICO would accept
- Letters and schedules generated
A subject access request gives you one month to find, read, and disclose the personal data you hold about someone, while protecting everyone else named alongside them. For most teams that means days of searching mailboxes, reading thousands of emails, and redacting by hand against a tight statutory deadline. Done in a hurry, it is also where third parties are disclosed by mistake and searches are quietly narrowed.
DSAR Automation does the mechanical work for you. It reads the request, takes in the data, removes duplicates, finds the people named in it, redacts third parties, checks its own output, and assembles the disclosure bundle, its index, the schedules, and the covering letter. What it never does is make the legal decisions. Privilege, contested third-party balancing, borderline relevance, and final sign-off are put to your people as review queues, with the evidence on screen and every decision logged.
It runs as an appliance inside your own environment and uses your own AI model. Documents and the requester’s details never come to Blackfoot.
Get a quote for DSAR Automation
Tell us your scope and objectives, and we’ll come back with a clear, fixed proposal, usually the same working day.
Get a Quoteor call +44 (0) 203 393 7795- CREST-accredited
- UK-based specialists
- Crown Commercial Service supplier
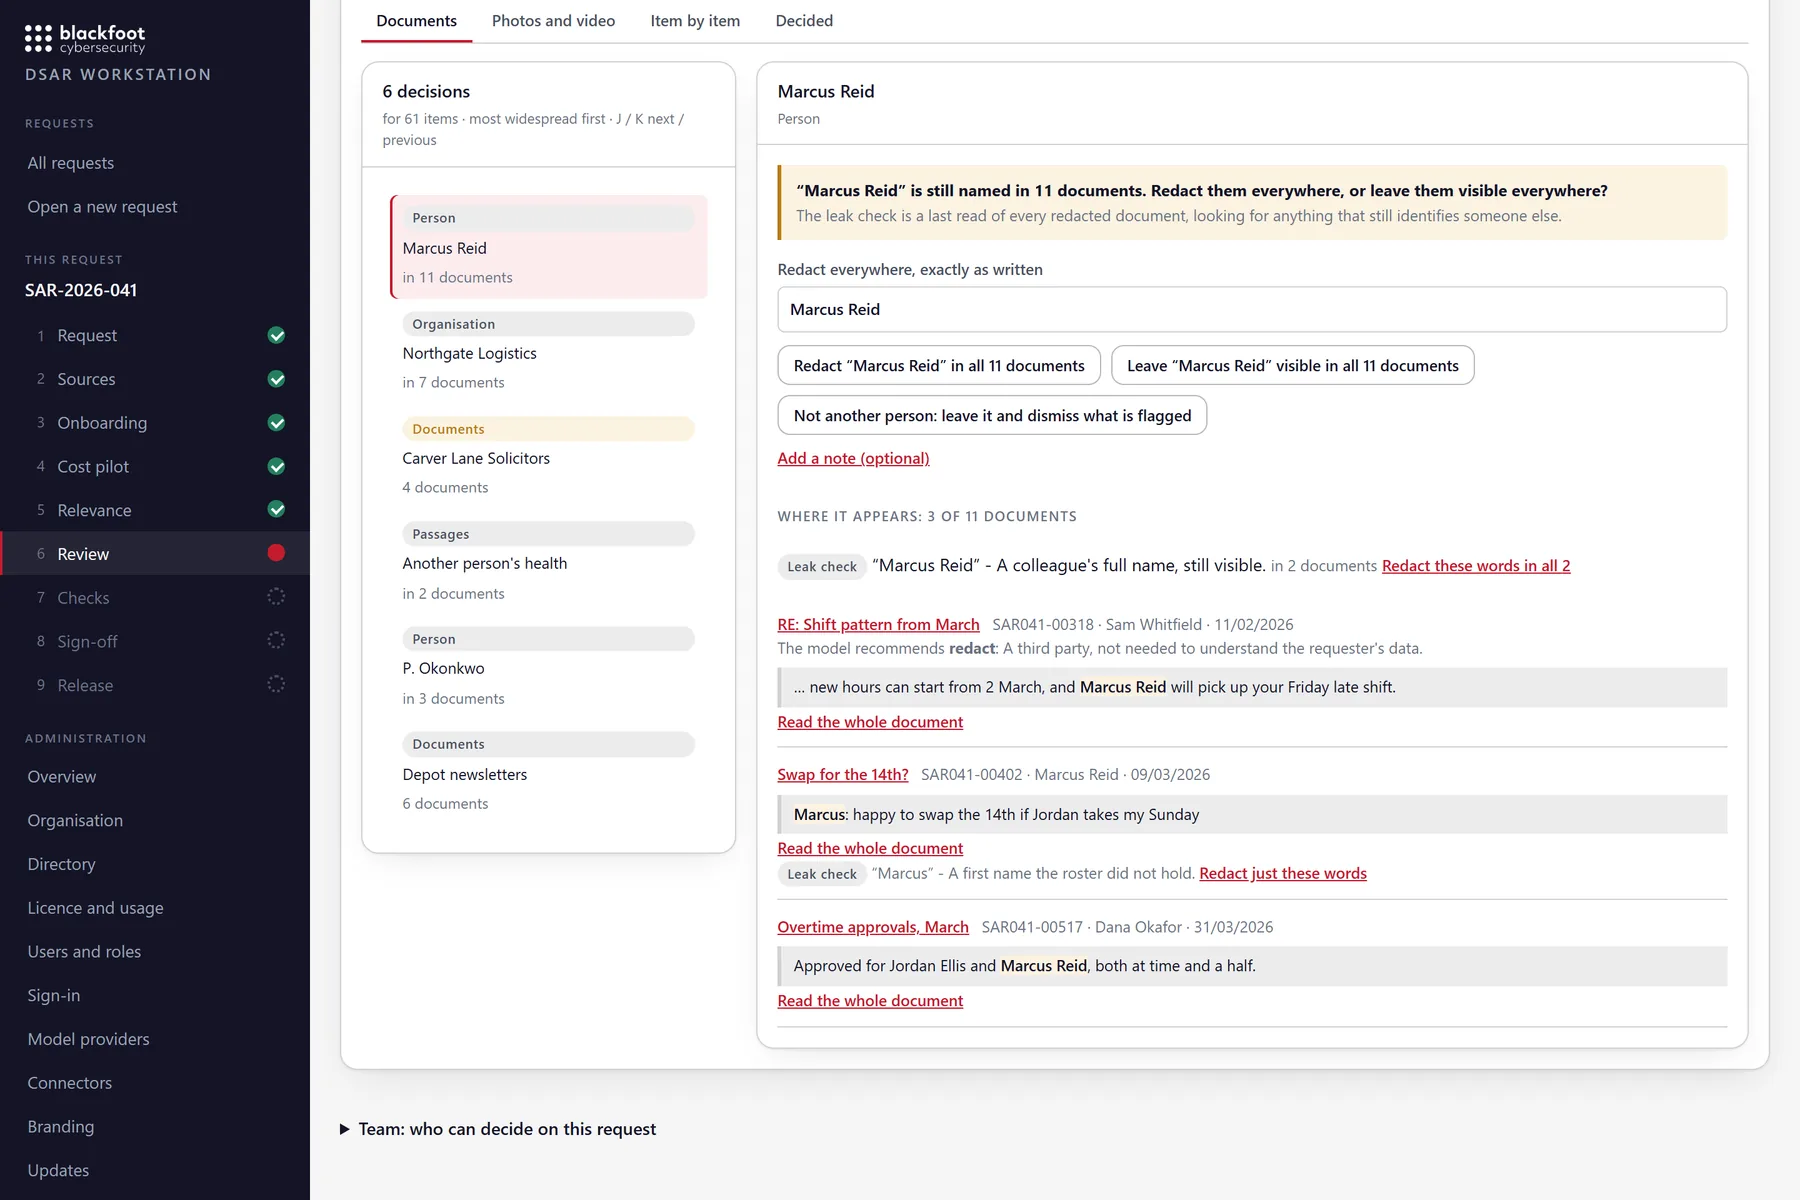
Inside the workstation
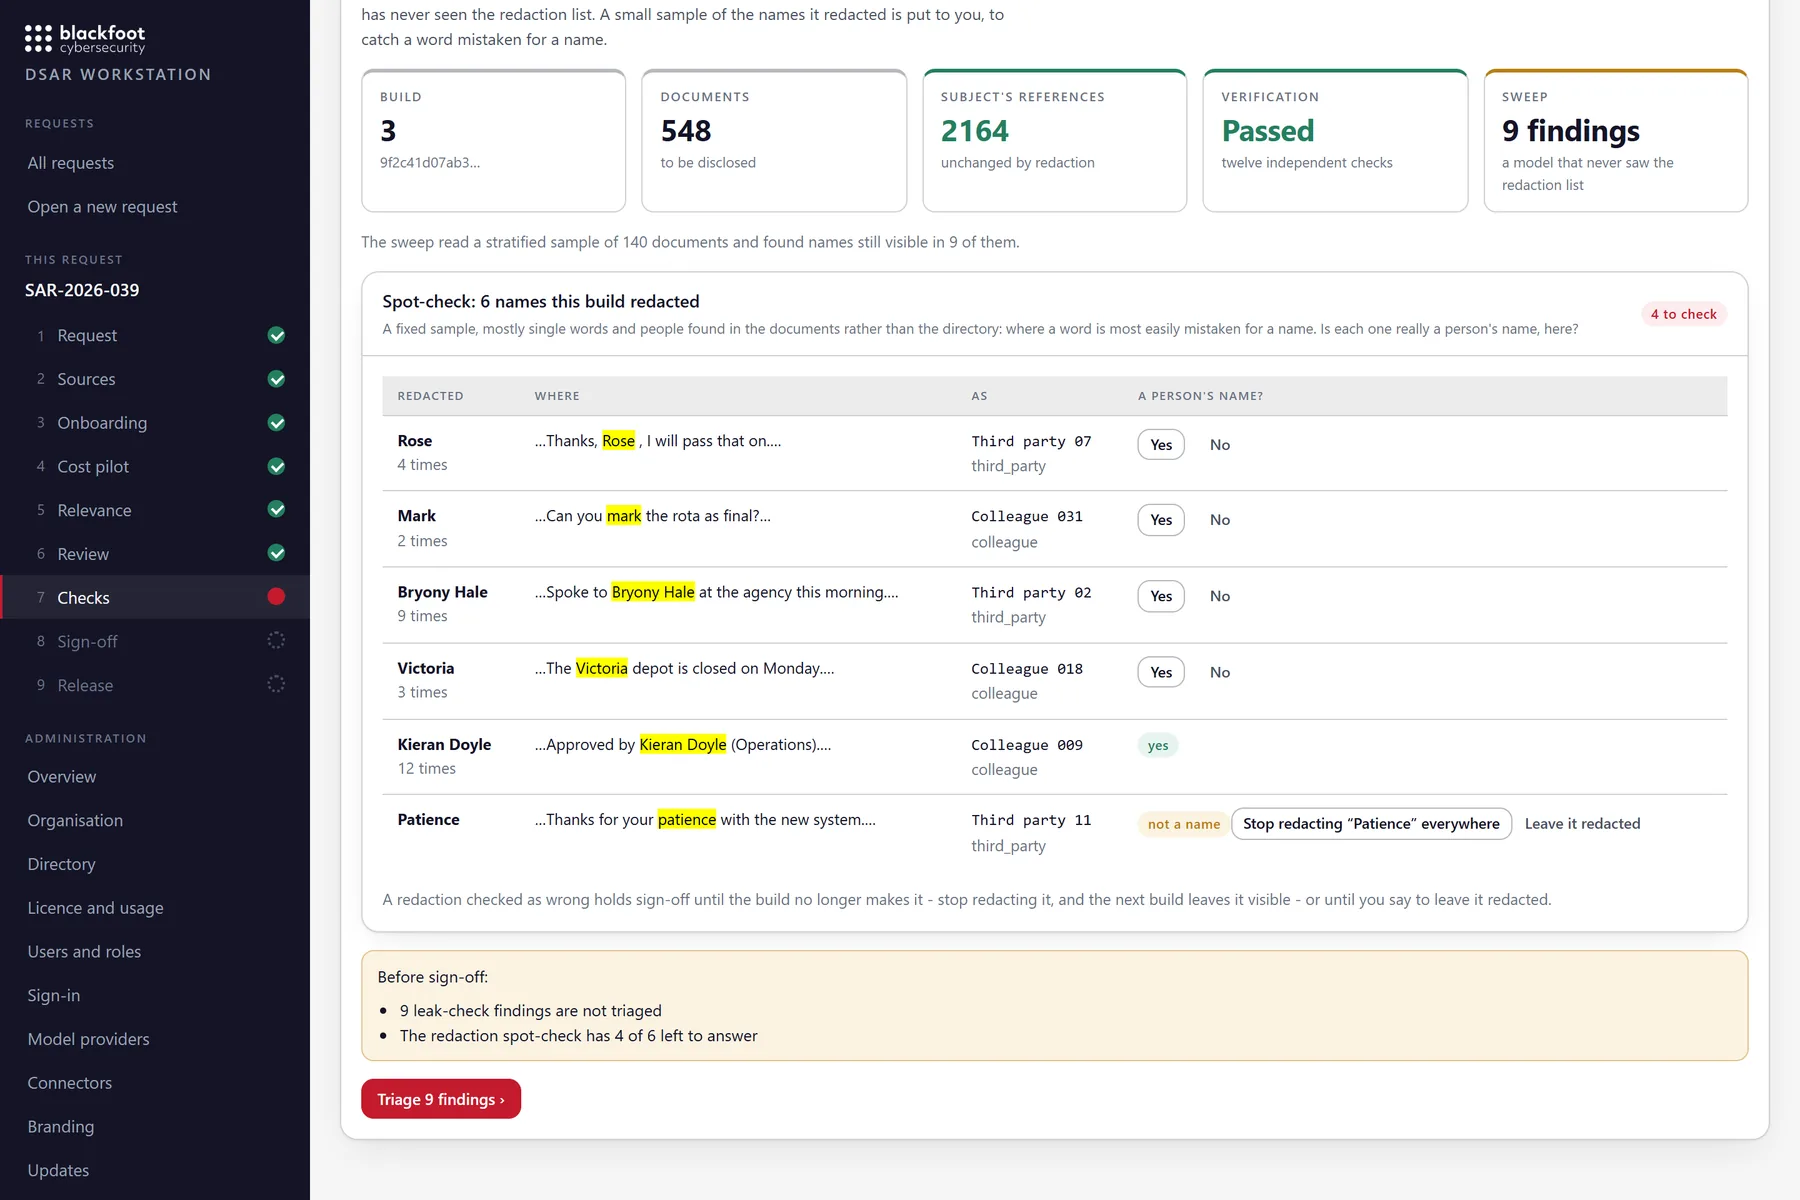
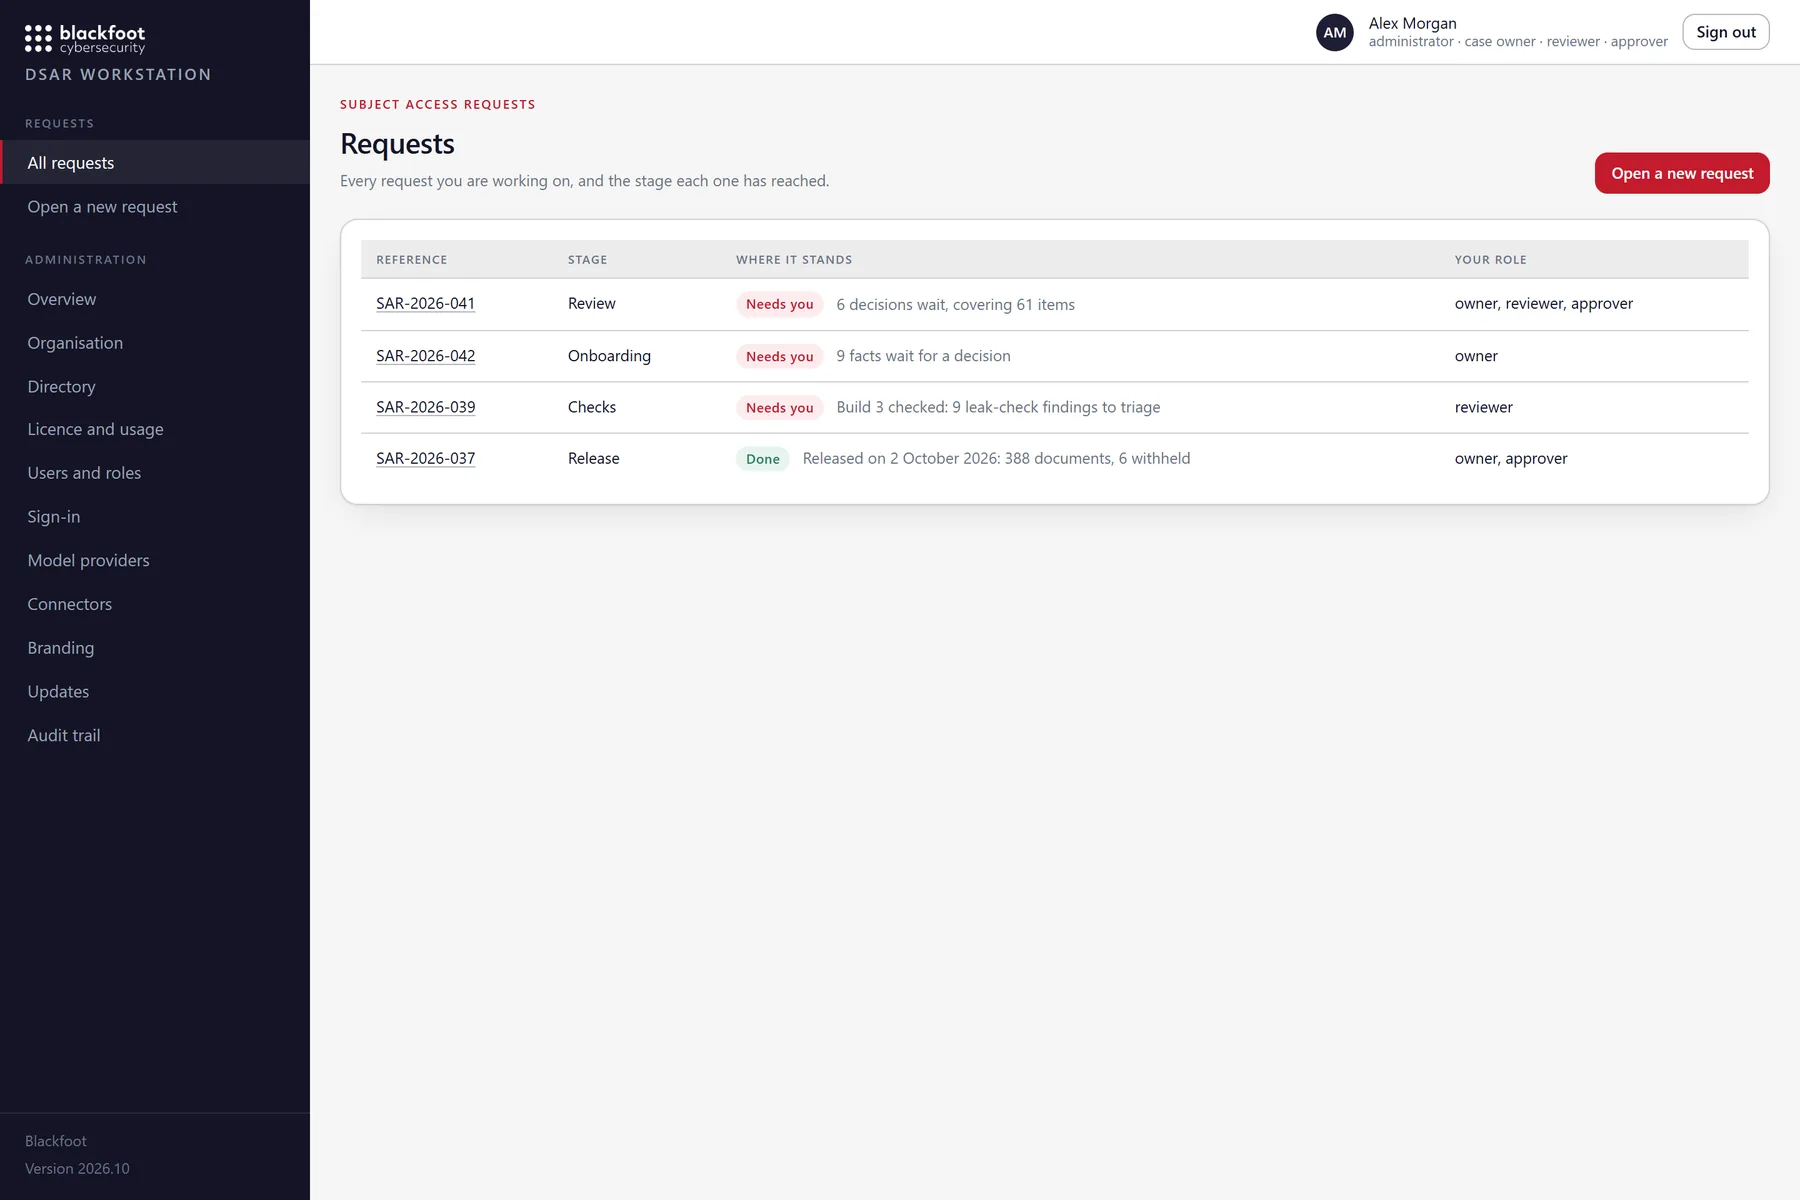
Built for the people who do the reading. Shown here with invented data.
How it works
- 01
Log the request
The request is read and the requester, their identifiers, what they asked for, and the statutory deadline are proposed, each beside the words it came from. A person confirms them before any data is searched.
- 02
Bring in the data
Upload a Microsoft Purview eDiscovery export, mailboxes, documents, and exports from HR or CRM systems, or collect them through connectors. Every file is hashed on arrival and the originals are never altered.
- 03
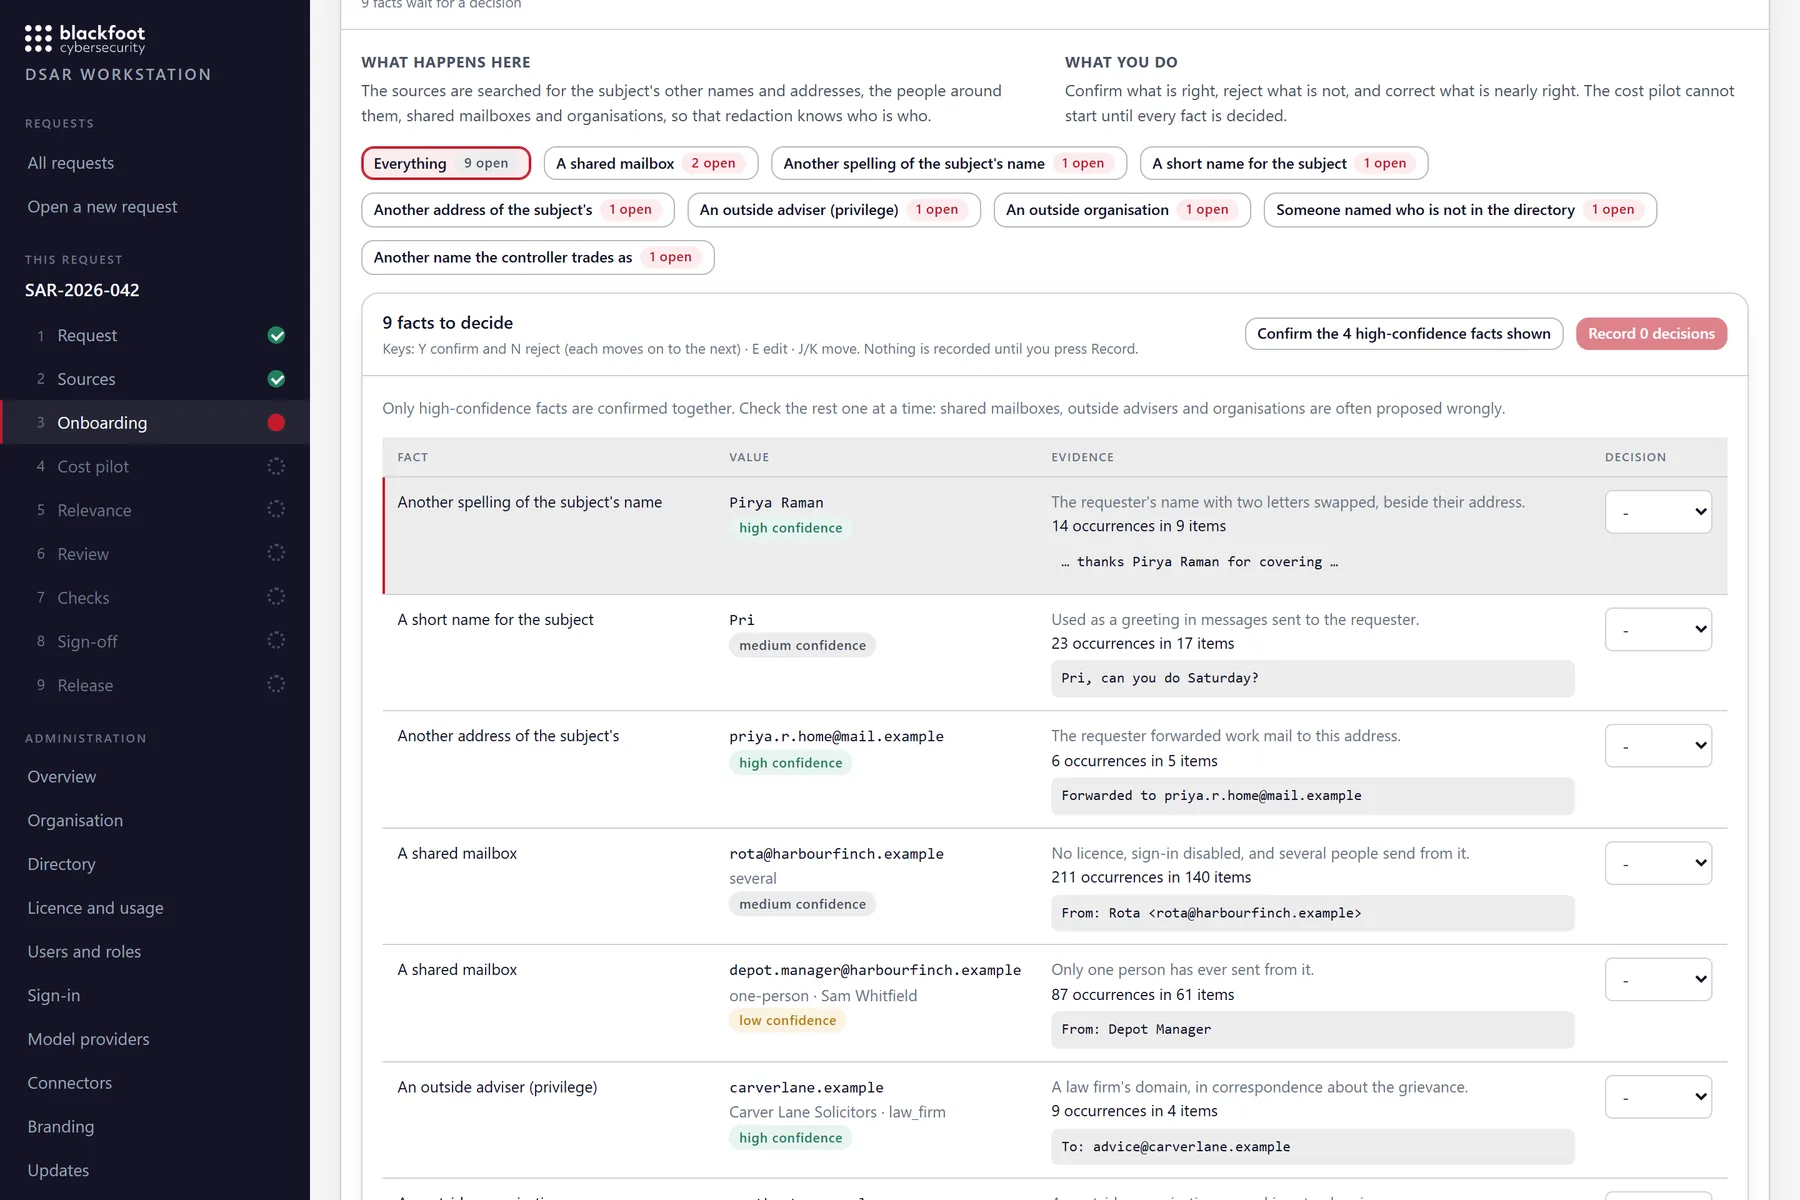
Confirm what it found
The product proposes the facts it discovered: spellings of the requester’s name, their addresses, shared mailboxes and who runs them, and the people the documents name. Your team confirms or rejects each one.
- 04
Work the review queues
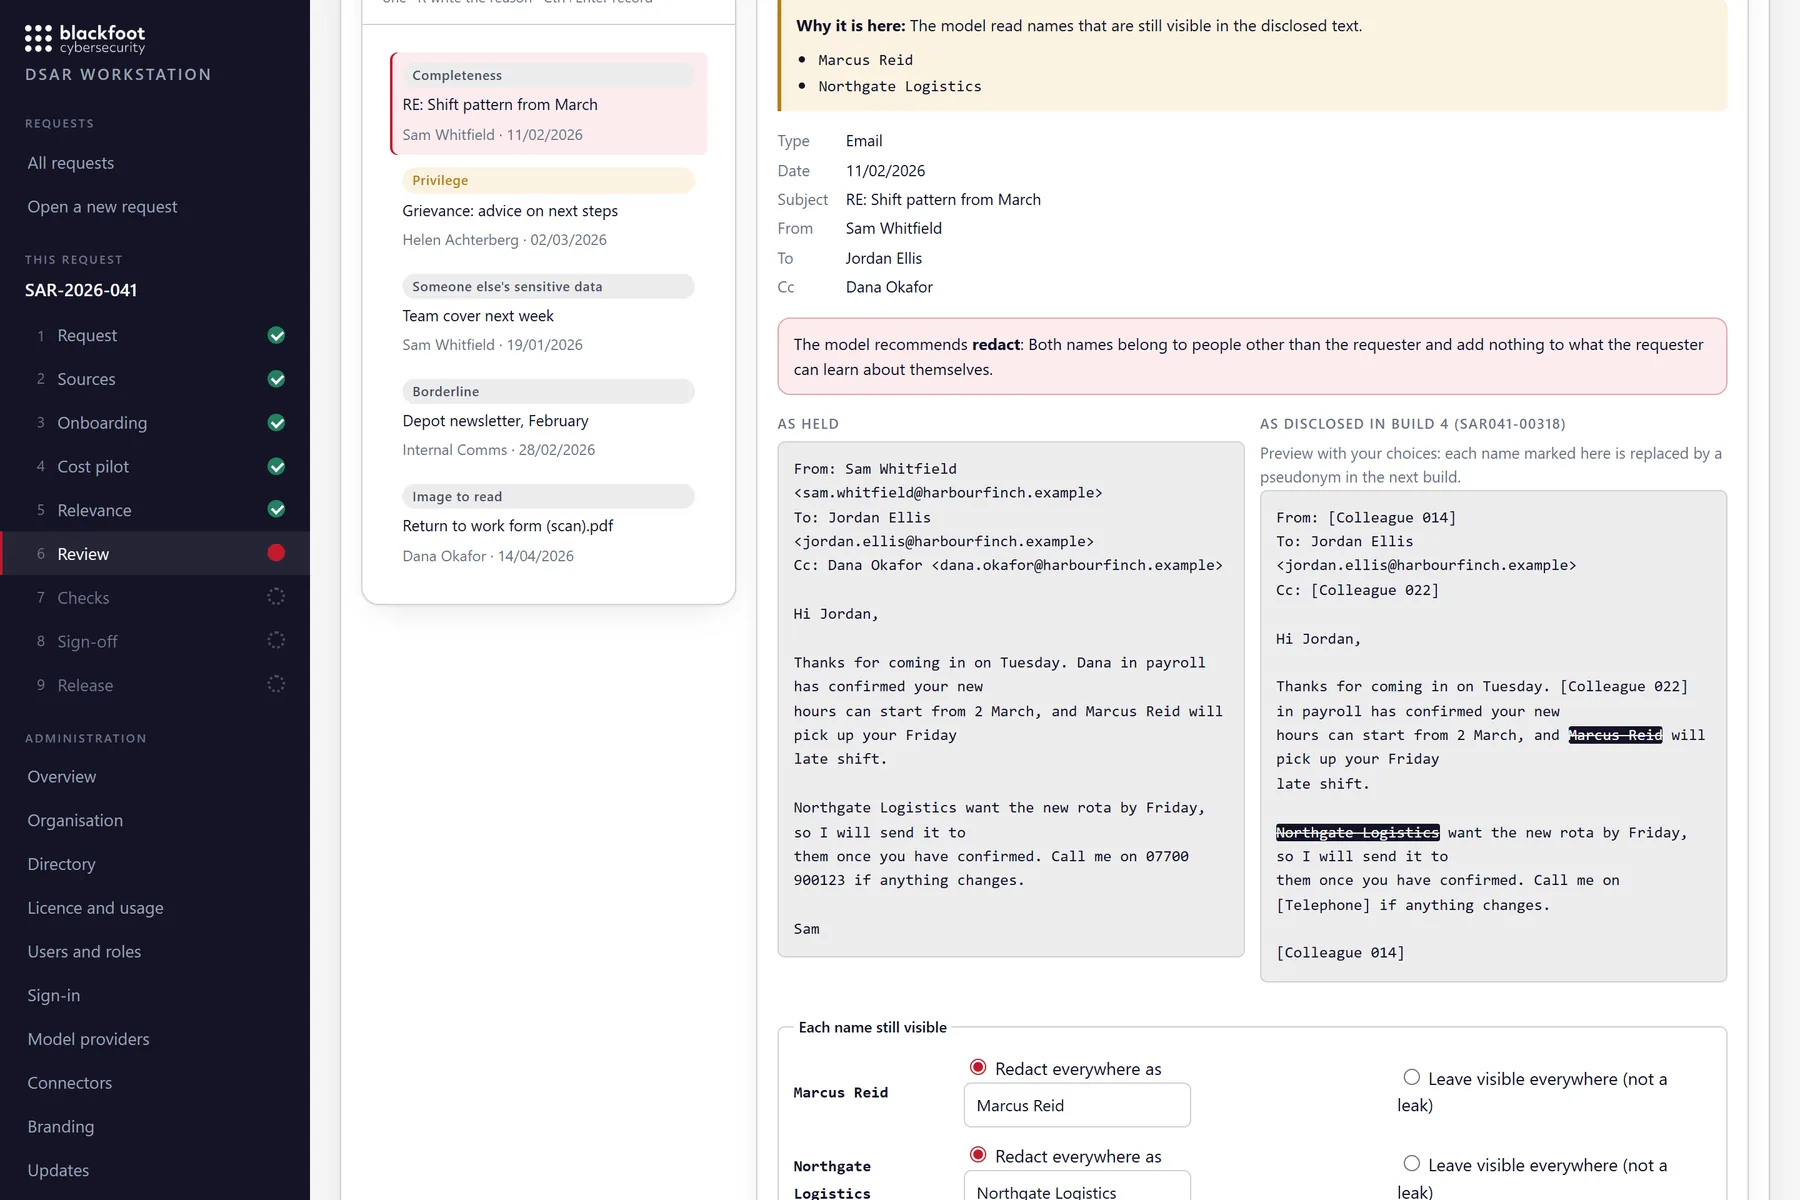
Privilege candidates, ambiguous names, borderline relevance, image-only documents, and people in photographs and video, each shown with the source and the redacted text side by side.
- 05
Verify and sign off
Every build is checked, including an independent sweep for anything the redaction missed. Sign-off is only possible when every queue is empty and every check has passed.
- 06
Release
The disclosure bundle, its index, the covering letter, the withheld schedule, the internal record, and the decision log are all generated from the build that was signed off.
Source and disclosure, side by side
Reviewers see every document as it was collected and as it will be disclosed. The requester’s own data is protected throughout, and every redaction names the rule that made it.
FromSam Whitfield
ToJordan Ellis
SubjectYour flexible working request
Hi Jordan, thanks for coming in on Tuesday. I spoke to Dana Okafor in payroll, who confirmed your new hours can start on 1 March. Northgate Logistics need the new rota by Friday, so I will send it once you have confirmed. Call me on 07700 900123 if anything changes.
FromRedacted: Third party
ToJordan Ellis
SubjectYour flexible working request
Hi Jordan, thanks for coming in on Tuesday. I spoke to Redacted: Third party in payroll, who confirmed your new hours can start on 1 March. Redacted: Client need the new rota by Friday, so I will send it once you have confirmed. Call me on Redacted: Phone if anything changes.
- Requester’s references: 2 before, 2 after
- Redacted: 2 people, 1 client, 1 phone number
Photographs and video, redacted in the pixels
Every face in every frame is found and compared with the requester. Only the requester stays visible. Everyone else is burned out of the pixels, and a face the engine is unsure of is redacted and put to a reviewer. Number plates and text are hidden too, and the sound is removed unless you choose a redacted transcript.
- Kept: the requester
- Redacted
- Unsure: redacted, and put to a reviewer
The product’s own output, run on a stock clip by Yan Krukau from Pexels.
Your data stays under your control
The whole product runs as one appliance inside your own cloud subscription or data centre, with your own sign-in. Documents and the requester’s details never come to Blackfoot: pseudonymised text goes only to the AI model you choose, in your own account and under its provider’s terms, and in connected mode we receive only the licence, version, and counts shown below. It was built by a penetration testing firm and threat-modelled on the assumption that you will test it.
- Pseudonymised text, after the governance gateYour AI modelMicrosoft Foundry, OpenAI, Anthropic, Gemini, Bedrock, Mistral, or self-hosted
- The requester’s search termsYour systemsPurview eDiscovery exports, file shares, CRM, HR, and ticketing
- Sign-inYour identity providerMicrosoft Entra ID or any OpenID Connect provider
What leaves the appliance, and what never does
| What leaves | Where to | Never |
|---|---|---|
| Pseudonymised document text and the request | Your own AI model, once the case has recorded your data processing agreement and the model’s retention terms | Blackfoot, or any model account we own |
| The requester’s identifiers, as search terms | Your own connected systems, which already hold the data | Anywhere else |
| Licence, version, and for each case a random identifier, dates, and counts | Blackfoot, at check-in, in connected mode only | Case references, names, addresses, any hash of them, documents, reviewers’ notes, or error text |
Security built in
Hostile input expected
Documents are treated as attacker-controlled. They are shown as text and never rendered as HTML, and parsed with limits on size, depth, and decompression.
Prompt injection contained
A model’s output is a proposal applied by deterministic code. It cannot trigger an action, widen a scope, or change a decision.
Access by role and by case
Roles come from your identity provider and count only on the cases a person is assigned to. Administrators cannot read a case they are not on.
Outbound traffic allow-listed
Only the worker can reach out: to your model, your identity provider, and your systems, and to our licensing service in connected mode only. Enforced at the network and in the application.
Encrypted at rest
Disks and storage are encrypted, optionally under your own key. Stored secrets are sealed, and only the worker can open them.
Tamper-evident audit
The audit trail is hash-chained, anchored off the machine daily, and has no free-text field, so document content cannot be logged by accident.
Fast where it can be, careful where it has to be
Every decision in a subject access request falls into one of three kinds, and the product treats each differently. Mechanical work, such as extraction, de-duplication, redaction, verification, and every figure in the covering letter, is fully automated. Configuration, such as who the requester is, every spelling of their name, and which shared mailboxes belong to one person, is discovered from your directory and the documents themselves, and your team confirms it rather than writing it. Legal and factual judgement is never automated, not even when a model is confident.
The time saved comes from the first two. The safety comes from the third: each judgement is one keystroke with the source beside it, and the record of who decided what, when, and why builds itself.
How it is priced
There is an annual platform licence, which covers unlimited users, updates, and business-hours support, and a one-off set-up that covers deployment, sign-in configuration, and training. Each request then carries a fee set by its size, in bands by the number of documents counted at ingest after duplicates are removed. You are never charged for copies of the same email, for rebuilds, or for re-runs, and there is no cap on size. A number of smaller requests each licence year carry no request fee at all.
Photographs count as documents. Video is priced by the minute, either as you go or through a media edition with a pool of hours for the year, which suits teams with regular CCTV or body-worn camera requests.
Your AI model and your hosting are billed to you directly by your own providers, so those costs stay under your control. Support beyond business hours, training, and expert help on a difficult request are available by the day or in prepaid blocks, never per case. The pricing is designed so that a team handling requests regularly spends less in total than it would doing the same work by hand.
What you get
The requester’s data protected
The requester’s own references are counted before and after every build. If redaction would remove any of them, the build is refused rather than released.
Redaction you can defend
Third parties, clients, and special category data are redacted by deterministic rules your team can inspect, and every build carries a spot-check, answered by a person, for words mistaken for names.
Photographs, video, and audio
Every face but the requester’s, people without visible faces, number plates, and text are redacted. A video’s sound can be removed, muted word by word, or replaced by a redacted transcript.
A record the ICO would accept
Every human decision is logged with who, when, what, and why, and a tamper-evident audit trail that holds no document content can be streamed to your SIEM.
Letters and schedules generated
Every figure in the covering letter, index, and withheld schedule comes from the signed-off build. The figures are generated; the wording around them stays yours.
Unlimited users
Case owners, reviewers, approvers, and administrators sign in with Microsoft Entra ID or any OpenID Connect provider, with no charge per seat.
Frequently asked questions
Straight answers to what prospective clients ask us most.
Does any of our data come to Blackfoot?
No. Documents, names, reviewers’ notes, and anything else in a case stay inside your environment, except the pseudonymised text sent to the AI model you choose, which is handled under that provider’s terms. In connected mode the appliance sends us its licence and version and, for each case, a random identifier, dates, and counts, so we can bill and offer updates. In offline mode it sends nothing, and you send us a sealed usage statement instead.
Which AI models does it use?
Yours. It works with Microsoft Foundry and Azure OpenAI, OpenAI, Anthropic, Google Gemini, Amazon Bedrock, Mistral, and self-hosted models with an OpenAI-compatible interface. Before a case sends any content, it records your data processing agreement and the model’s retention terms, and the text is pseudonymised against your directory first.
Will the AI decide what we disclose?
No. A model may propose, for example that a name belongs to a third party, but its proposals are applied by deterministic code and checked. Privilege, contested balancing, borderline relevance, and sign-off are always decided by a person.
Where does it run?
On any Linux host with Docker in your own cloud subscription or data centre, typically a single virtual machine. There is a scripted deployment for Microsoft Azure, and updates arrive as signed bundles that are verified and backed up before they apply, and can be rolled back.
What happens if our licence lapses in the middle of a request?
Requests already open carry on to release. A lapsed licence only stops new cases being opened, so a statutory deadline never depends on our servers or a renewal.
Will Blackfoot run the request for us?
Your team runs every request and signs it off, which keeps the decisions with the controller. We set the platform up, train your team, and provide support. For a difficult request we can work alongside you as a guest in your own workstation, and our External DPO service can advise on validity, timelines, and exemptions.
Insights and case studies
Related services
Ready to talk about DSAR automation?
Get a fixed-scope quote, usually the same working day.